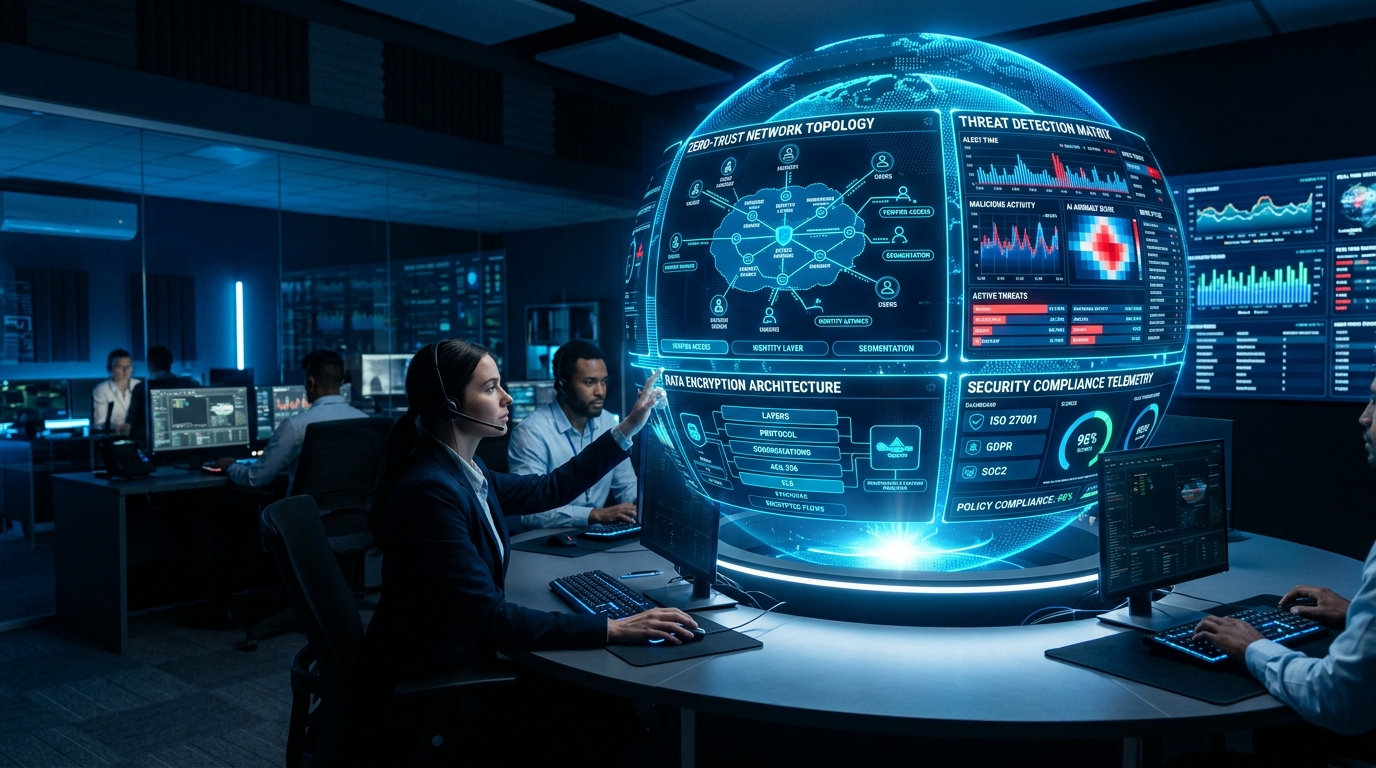
Embedding Zero-Trust Security & Continuous Regulatory Governance
From automated DevSecOps and cloud posture management to SOC 2, HIPAA, and ISO 27001 readiness, Nivedis embeds proactive security guardrails into every layer of your engineering lifecycle and data infrastructure.
Security that stays ahead of threats.
Comprehensive Security Audits
Deep-dive assessments of your cloud configurations, codebases, API gateways, and data flows — pinpointing vulnerabilities before they can be exploited.
Continuous Threat Detection
Proactive monitoring, SIEM integration, and automated vulnerability scanning that keeps you ahead of evolving attack vectors — not reacting after breaches.
Regulatory Compliance Programs
Tailored governance frameworks aligned to ISO 27001, GDPR, and SOC 2 Type II — designed cleanly around your data flows, contracts, and industry duties.
Business Resilience by Design
Disaster recovery architectures, automated backup validation, and incident playbooks so your operations absorb disruption and recover within minutes.
Compliance built on proven standards.
From exposure to enterprise resilience.
Security Posture Assessment
We evaluate your current configurations, IAM boundaries, encryption protocols, and policy gaps to construct a clear, prioritized risk matrix.
Remediation & Controls Build
We deploy automated guardrails, secret management, CI/CD scanning, and policy documentation to close exposures without choking release velocity.
Continuous Validation & Auditing
Automated regression tests, compliance evidence collection, and quarterly red-team reviews ensure your security evolves alongside threats.
Security delivered with pragmatic rigor.
Direct collaboration with practitioners, radical transparency, in-repo commits, and 100% intellectual property ownership.
Schedule a Security & Compliance Strategy Call
Speak directly with a Principal Security Architect. Bring your vulnerability report, audit deadline, or SOC2/HIPAA goals — we'll map a concrete remediation plan with zero sales pressure.
Direct consultation with lead DevSecOps and compliance practitioners.
All architecture diagrams, policy reviews, and vulnerability notes are strictly protected.
100% compliance runbooks, hardening scripts, and audit reports owned by your team.
Request a Security & Compliance Audit
Direct review by our principal security engineers.